CISSP Renewal – 7 Paths to Renew CISSP Certification
CISSP renewal requires certification holders to earn 120 CISSP CPE credits every three years. There are certain ISC2 CPE requirements and categories to earn CISSP CPE credits. We’ve explored the seven CISSP renewal steps in this article.
In this article
📌 Hint: Do not skip this article; you will find FREE CISSP Renewal CPE resources throughout the article.
Before diving into the best paths to earn CISSP CPE credits, you need to know the CISSP renewal requirements and which activities can earn you CPE hours to renew your CISSP certification. You might be interested in reading our 7 Ways to Get CISSP CPE Credits article as well.
What is the Easiest Way to Renew CISSP Certification?
You’ve landed on a comprehensive CISSP renewal article; however, if you do not have that much time and want to cut to the chase, here is the point. The most comfortable and affordable way to renew your CISSP certification is to attend an online 120 CISSP Credits course. Let’s explain why.
ISC2 requires CISSP certification holders to earn 120 CPE credits every three years. You will read the details of CISSP CPE requirements below in detail. Typically, 1 CPE is earned by attending a one-hour activity. Consider yourself attending a two-day cybersecurity conference. Typically, you will earn around 12 CISSP CPE Credits. However, such a conference is ticketed around 1,500-2,000 USD. Besides, you have to travel to another city if it is not in your city. Is it easy for a full-time professional to attend these types of activities 10 times every three years? I think I know your answer.
Easiest Way to Earn 120 CISSP CPE Credits at Once
We’ve explained the easiest, most comfortable, and affordable way to earn 120 CISSP CPE Credits in our video.
5 Benefits of Attending an Online CISSP Renewal Course
Here comes the comfort of attending an online 120 CISSP CPE Credits Course:
- Earn 120 CISSP Credits at once. You will read further in the article that there is a difference between Group A and Group B CPE activities. There is a cap for Group B activities: you cannot report more than 30 CPEs every three years, while you can submit all CPE credits from Group A. If you attend an online ISC2 CPE course, you won’t need to care about the caps and limits. You will earn all required CPE credits from one resource.
- Earn CISSP CPE Credits at your pace, in your place. Online CPE credit courses are self-paced. You will follow the recorded lectures at your place, either from your home or office, at any time you are available.
- Pay much less compared to offline activities. Considering a cybersecurity conference is roughly ticketed at 1,000 USD per day, you will pay at least 15,000 USD for 20 conferences to earn 120 CISSP CPE credits. However, you can pay around 300 USD and earn all 120 CPE credits at once by attending an online CISSP Renewal Course.
- Spend less effort. By attending an online CISSP CPE Credits course, you will just pay the course price, follow the lectures, and earn CPE credits. For other CPE activities, you have to attend a conference, prepare a presentation, or volunteer in an organization, etc.; each of them requires much more time.
- Less Probability of Hitting ISC2 Audit. Since the courses are already attended and submitted by hundreds of thousands of CISSP certification holders, there is already a track of CPE reporting at ISC2. Therefore, they are less likely to be audited by ISC2 compared to other activities.
These are the main reasons why we favor attending online CISSP CPE credit courses to renew CISSP certification for working professionals.
Can I Renew CISSP Certification for FREE?
To renew your CISSP certification, you need to earn 120 CPE Credits. Typically, you can attend some free webinars to earn CPE credits. However, typically, they are typically one hour long, and you will earn 1 CPE from one webinar. There are other opportunities like volunteering, reading, or presentations (you can read further below); however, finding relevant resources or organizations for them is not easy. Therefore, it is not easy to find several webinars to earn all CPEs from free activities.
At San Francisco Business School, we also offer a Free ISC2 CPE Credits Online Course. You can attend and earn 3 CPE credits. While you will have the opportunity to look at our courses, you can consider attending the 120 CPE Credits course afterwards.
Note that even if you earn all 120 CPE credits to renew your CISSP certification, there is still an Annual Management Fee (AMF) that you must pay to ISC2. Annual Management Fee (AMF) is 125 USD per year to keep your status and certification active at ISC2. If you pay the AMF, there is no additional fee to renew your CISSP certification. Once you have earned and reported 120 CPE credits, you will be able to renew your CISSP certification.
Now, let’s focus on CISSP Renewal Requirements and 7 ways to earn CPE credits to renew CISSP Certification.
CISSP Renewal CPE Requirements
CPE is the abbreviation of Continuing Professional Education. Typically, an hour spent on an activity equals one CPE credit. You can report CPE credits in 0.25, 0.50, and 0.75 increments. For instance, if you attended a 30-minute webinar, you can earn 0.5 CPE credits.
ISC2 requires CISSP certification holders to earn 120 CISSP CPE credits in a three-year period.
| Certification | CPE Category | Suggested Annual CPEs | 3-year Total |
|
CISSP
|
Group A | 30 | 90 |
| Group A or B | 10 | 30 | |
| Total Required | 40 | 120 |
CISSP Renewal Fee
There is also an Annual Management Fee (AMF) of 125 USD per year that every CISSP certification holder must pay. Note that this is an annual membership fee to keep your certification and status active on ISC2. You will not be paying an additional CISSP certification renewal fee if you paid AMF every year. So, a three-year CISSP renewal will cost you 375 USD on keeping ISC2 account active.
ISC2 has further requirements for the 120 CISSP renewal credits. There are two groups of CPE categories to earn CPE credits. Group A and Group B. ISC2 requires 90 CPE credits to be earned from Group A and 30 CPE credits from the Group B category.
Group A credits: domain-related activities
Group A credits relate directly to activities in the areas covered by the specific domains of the respective credential. For the CISSP certification renewal, these activities should be related to information security, information management, business management, etc.
You can earn Group A CISSP Credits through the following example activities:
- Education: Taking an online course such as CISSP Renewal Courses (*Most Popular)
- Reading a cybersecurity white paper
- Publishing an article on cybersecurity
- Attending ISC2 Security Congress
- Preparing for a presentation or teaching information related to cybersecurity
- Performing a unique work-related project that is not part of your normal work duties
- Self-study related to research for a project or preparing for a certification examination
- Volunteering for government, public sector, and other charitable organizations
- Taking a higher education course
We will go through each of these paths to earn CISSP Renewal CPE credits in detail throughout this article.
Note that your day-to-day work activities do not count for CISSP CPE credits even if your job includes information security activities.
Watch the 7 Paths to Earn CISSP Renewal CPE Credits Video
We’ve listed the 7 paths to earn CPE credits in our following YouTube video.
Group B credits: professional development
Group B credits are earned for completion of general professional development activities that enhance your overall professional skills, education, knowledge, or competency outside the domains associated with your respective certifications. This can include programs such as professional speaking or general management courses. While these do not apply directly to the domains, ISC2 recognizes that these skills are vital in the growth of all professionals.
You can earn Group B CISSP Renewal Credits through the following example activities:
- Attending non-security events, such as leadership conferences
- Participating in non-security education courses such as Business Strategy Training.
- Preparing for non-security presentations/lectures/trainings
- Non-security government/private sector/charitable organization committees
Now, Let’s go through each CISSP CPE Credit earning path one by one.
1st Path – The Best Way for CISSP Renewal – Education
As we’ve highlighted in the previous section, earning CISSP CPE credits through the Education category is the most popular way for professionals.
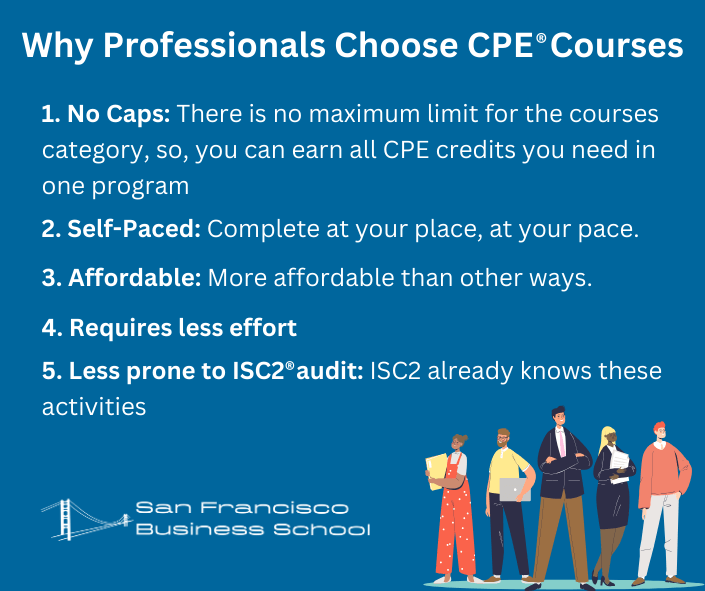
While there are several benefits of CISSP renewal through CPE courses, here are the top five reasons:
- No Caps: There is no maximum limit for the Education category, so, you can earn all CISSP CPE needs in one program, and renew ISC2 certification. You do not need to go elsewhere to find additional CPEs to renew CISSP certification.
- Self-Paced: You do not need to attend an event, conference, or seminar. You can follow the courses at your place, at your pace.
- Affordable: Depending on the program content, you can enroll in a self-paced CISSP CPE Online Training for ~$200-300. However, seminars or conferences start from $1,000, not only that, you may not earn all CPE needs in one event.
- Requires less effort: When you enroll in CPE Courses, all you have to do is follow the curriculum, earn CPEs, and renew your CISSP certification. However, other CPE credits earning paths require significant effort from the CISSP certification holder such as creating content, sharing a presentation, authoring, etc.
- Less prone to ISC2® audit: Since the CISSP renewal training programs are used by many certified professionals, ISC2 already has a track and record of the activities. However, for other categories, CPE submissions are more unique and may be more likely to hit an audit.
ISC2 CPE Online Courses to Renew Your ISC2 Certification
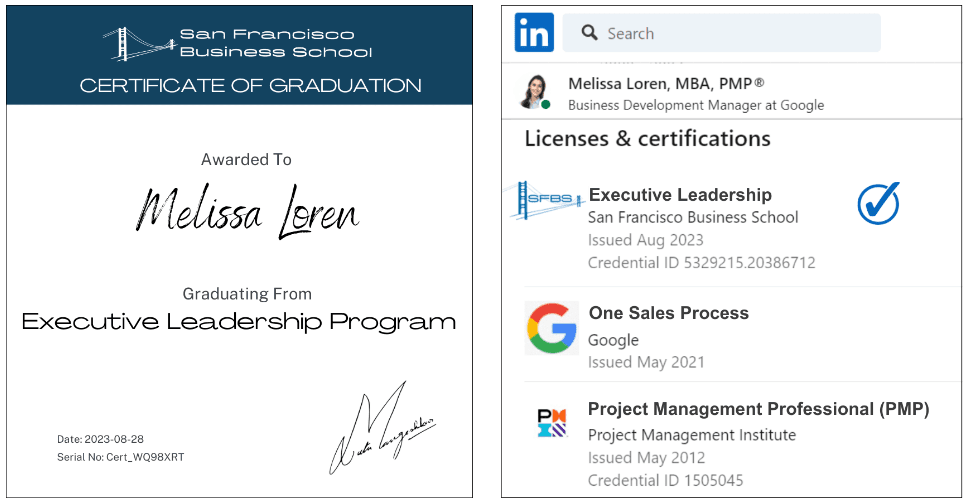
San Francisco Business School offers ISC2 Certification Renewal Course programs. The ISC2 CPE Training Programs by SFBS come with six self-paced cybersecurity and business training programs: AI & Cybersecurity, Machine Learning Principles for Secure Systems, Cybersecurity Best Practices for AI Systems, Executive Leadership, Strategy Creation & Execution, and Marketing Strategy. For each course in the programs, SFBS awards a certificate of graduation. While earning CPEs, you will earn reputable business merits to highlight in your resume and LinkedIn.
There is a CPE rule for Education CPE credits. You can submit a maximum of 40 CPE credits per entry. While you can earn all 120 CPEs through the education category, you need to submit at least three different entries.
Watch Kathy’s CISSP Renewal Journey
Kathy Buckley is a CISSP-certified Professional. Kathy enrolled in the 120 CISSP CPE Course Program from SFBS and renewed her CISSP. Watch now her CISSP renewal journey.
2nd Path for CISSP Renewal – Reading
ISC2 accepts CPE credits by reading cybersecurity white papers, books, magazines, or white papers. For instance, reading a cyber security blog, a business education blog, or a book can count CPEs toward renewing your CISSP certification. 1 hour of reading counts as 1 CPE, however, everyone’s reading pace is different. So, earning CISSP renewal CPE credits through reading resources is not a crystal clear way to go.
There are further requirements for earning CPEs through reading as well. A maximum number of CPE credits applies to the following activities:
- Books – 5 CPE credits per book with a 250-word description
- Magazines – 5 CPE credits per magazine issue with a 250-word description
- White papers – 1 CPE credit per paper with a 250-word description
So, there is a limit to earning CPEs through reading.
3rd Path for CISSP Certification Renewal – Events
Several cybersecurity conferences, events, and activities are organized throughout the year. Some of the events that can earn you CPE credits are as follows:
- Attending ISC2 Security Congress
- Industry conferences (in-person or virtual) and seminars
- Online webinars, podcasts, and other virtual offerings
- Professional cybersecurity chapter meetings
- Attending non-security events, such as leadership conferences
You can attend these events and earn CISSP CPE credits. Typically, a one-day activity earns 6 CPEs. So, if you attended a two-day event, you will earn around 12 CISSP renewal CPE credits.
Attending global events has benefits like expanding your professional network and learning the changing trends in your domain. However, there are some pitfalls to these events.
- Typically organized in big cities. If you are living in a relatively smaller city, you might not see any events to earn CPEs.
- Requires in-person attendance. Many of the events take a few days, and you have to take days off from your work to attend these events.
- Expensive. Typically, these events are charged $1,000/day. So, for a two-day event, you need to pay around $2,000. Travel and accommodation, if needed, are not included in these fees.
- Does not earn CPE credits at once. Although it requires a significant amount of time and money, you cannot earn all the required CPE credits you need through one event.
Considering you are a full-time working professional and looking to earn CISSP renewal credits in one step, we do not recommend this path for earning CPEs.
San Francisco Business School offers a self-paced Free ISC2 CPE Course Online Program as well. If you attend this program, you can earn 3 Free CISSP CPE credits and submit them in the education category.
4th Path to Renew CISSP Certification – Authoring
If you are authoring business or cybersecurity-related content, ISC2 accepts your activity as a source of CPE credits. Some of the activities you can earn CISSP CPE credits are as follows:
- Publishing an article on cybersecurity
- Preparing for a presentation or teaching information related to cybersecurity
- Preparing for non-security presentations/lectures/trainings
- Writing, researching, and publishing books, articles, papers, and blogs
- Preparation time for webinars, podcasts, or presentations
- Preparing new or updating existing training seminars or classroom materials
Do you write articles or blogs? Give webinars? Make videos? Today’s digital world is full of new content and anything you create counts towards your CISSP renewal process. Typically, you can submit CPEs for the hours you worked on content creation. For instance, if you wrote a blog post for an hour, you can claim 1 CPE credit in your ISC2 profile.
Creating content is cumbersome. There are several aspects of curating quality content. If your profession involves creating content, it is fine, you can earn CISSP CPE credits while you are working. However, just to earn CPEs, creating content is a tough path.
CPE rules for Authoring
There are further CPE rules for authoring activities. A maximum number of CPE credits applies to the following activities:
- Books: 40 CPE credits per book as author, 20 CPE credits per book as co-author, 10 CPE credits per book as editor
- Articles: 20 CPE credits per article as author, 10 CPE credits per article as co-author, 5 CPE credits per article as editor
- Chapters in books: 20 CPE credits per chapter as author, 10 CPE credits per chapter as co-author, 5 CPE credits per chapter as editor
- Professional blogs: 10 CPE credits per blog as author, 5 CPE credits per blog as co-author, 2 CPE credits per blog as editor
- White papers: 10 CPE credits per white paper as author, 5 CPE credits per white paper as co-author, 2 CPE credits per white paper as editor
- Preparing existing training: one-day course equals 2 CPE credits, two-day course equals 5 CPE credits, five- to seven-day courses equals 10 CPE credits, and semesters (12 or more weeks) equal 20 CPE credits.
If you are authoring and trying to earn CPE credits, make sure you do not exceed these limits.
5th Path for CISSP Renewal – Unique Work Experience
ISC2 Members and Associates can earn up to 10 Group A CPE credits for activities performed during their regular working hours when they are engaged in unique projects, assignments, activities, or exercises. The unique project, assignment, activity, or exercise must fall outside their normal (or day-to-day) job responsibilities or job description.
For instance, if you are helping a charity organization audit its website vulnerabilities, this can count as a unique work experience and you can earn CISSP renewal CPE credits. One hour of participation related to the credential domains equals 1 CPE credit with a maximum of 10 CPE credits per unique work experience.
6th Path to Earn CISSP Renewal Credits – Self-Study
If you are working on a research project, or if you are preparing for another certification examination, you can count your self-study hours as CPE credits. Depending on the topic you are working on, it can count as Group A or Group B CPE credit.
Cybersecurity-related research and certification examination preparations count toward Group A CPE credits. All other business-related work counts for Group B CISSP CPE credits.
7th Path to CISSP Certification Renewal – Volunteering
ISC2 accepts volunteering activities as CISSP CPE credits as well. Below are two examples of volunteering activities:
- Volunteering for government, public sector, and other charitable organizations
- Non-security government/private sector/charitable organization committees
You can search for volunteering options on the ISC2 website as well. Note that, these activities may not be available in your location if you are living in a small city.
Auditing of CPE credits
ISC2 CPE auditors perform random audits of submitted CPE activities by CISSP certification holders. Certification holders will need to provide proof of attendance or a brief description of the activity. This is an important process that upholds the integrity of ISC2 credentials and maintains compliance with ANSI/ISO standards for certification.
If your CISSP renewal CPE submissions are selected for an audit, you will receive an email with instructions about the necessary documentation to support the activities. It is important to respond to this request and provide the information exactly as instructed within 90 days.
Upon providing relevant documentation to ISC2, your application will be reviewed and CPE credits will be processed on your account.
Summary
CISSP certification holders need to earn 120 CPEs every three years to renew their certification. There are Group A and Group B categories for earning CPE credits. Group A activities are domain-related activities mainly around cybersecurity. Group B activities are non-domain related activities that can be about business topics and personal development.
Although there are 7 different paths to earn CISSP renewal CPE credits, the most popular way is attending CISSP CPE courses. Professionals choose CISSP CPE courses mainly because there is no cap, affordable, and easy to earn CPEs. Besides, CISSP CPE courses are less prone to audits as those activities are already known by ISC2.